I Gave 14 LLMs AWS Keys. Here’s What They Wanted to Do Next
What models propose after a cloud compromise, and the detections we can build from it
How attackers operate in AWS, more and more with AI, and practical ways to detect, deceive and contain them.
39 articles since 2022 · featured 22 times in 6 security newsletters
Featured research
With no AWS-specific guidance, an AI agent went from a leaked key to data exfiltration in about a minute, in 7 of 12 runs. An alert would most likely arrive after the damage is done.
Fourteen models, thirteen post-compromise scenarios. They ran the old playbook at machine speed: existing detections still work, and now we know which ones they trigger most.
Archive
What models propose after a cloud compromise, and the detections we can build from it
LLM models, and everything around them, are advancing fast, much faster than many of us can keep up with.
It’s well known that one of the most common ways attackers gain persistence in an AWS account after compromise is by creating a new IAM user, attaching an Administrator policy,…
It frustrates me that Detection Engineering still feels fragmented when it comes to the context and links between threat intelligence, detection ideas, and detection rules, and in…
While I was reading about the new AWS features released during the “pre:Invent” season, I noticed the new aws login command.
A penetration test report can build trust or destroy it.
When Anthropic announced “Automate security reviews with Claude Code” I was curious to see how it worked.
On July 8th, AWS announced Amazon Bedrock API keys to accelerate AI development. This new functionality includes new long-term API keys and short-term API keys.
This is a super‑brief review of my notes and some information from the talks I managed to attend.
I’m really happy to announce my latest tool: TrailAlerts, a serverless cloud-detection tool that lets you define simple rules (written in open Sigma syntax) as code and get rich…
Discover how attackers can abuse AWS CodeBuild and GitHub Actions to gain stealthy persistence in compromised AWS environments.
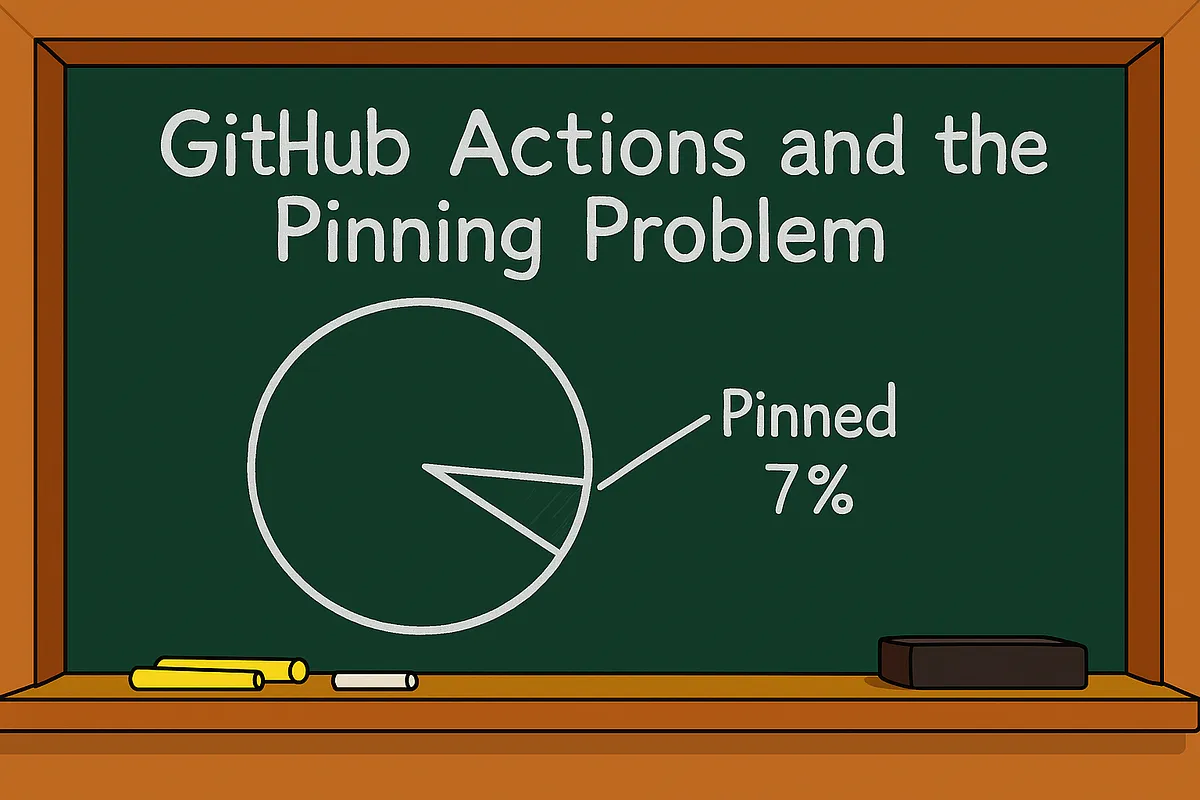
Only 7/100 popular security projects pin everything. Here’s what I learned digging into the data.
While in my previous articles from the DIY series, I explored how to build solutions with LLMs (Using Semgrep with LLMs and Building a…
DIY code reviews: Using open-source Semgrep + AWS Bedrock AI to auto-suggest fixes for vulnerabilities.
A breach in AWS isn’t game over, initial access is just the first move. Learn how to rig the game and win.
Security questionnaires are very common today. When customers consider your product, especially if you’re a startup, they often ask for…
My last two articles (how attackers can abuse IAM Roles Anywhere for persistent AWS access and gaining AWS persistence by updating a SAML…
When AWS introduced IAM Roles Anywhere in July 2022 (AWS Announcement), I made my first contribution to Stratus Red Team. I believed this…
After investigating potential post-exploitation attacks against various AWS services such as CloudFront, AppSync, and ALB, this article…
When an attacker compromises an AWS account, one of the first tactics they will try is gaining persistence. This is because, in many cases…
On August 9th, Christophe from Datadog released Grimoire during the DEFCON Cloud Village talk titled “Catch Them All! Detection Engineering…
When responding to incidents, especially in the cloud, every second matters as large parts of the attack might be automated. Because of…
I’ve always been a big fan of deception and honeypots. Even my final degree project was about implementing a honeypot with active blocking…
First and foremost, I want to say a big thank you to everyone who has taken the time to share, use, or comment on TrailDiscover. It’s been…
I’m excited to announce the launch of TrailDiscover, a new initiative to gather CloudTrail events linked to security incidents or actions…
Last year, I wrote about the importance of understanding risks in cybersecurity and the critical role of risk reduction. Recently, I’ve…
In my previous articles, I’ve explored various AWS services from an attacker’s viewpoint, discussing potential post-exploitation attacks…
In our ongoing exploration of post-exploitation attack vectors within AWS services, we’ve previously examined potential attacks against…
After my last article, where I explored unconventional methods attackers might employ to compromise an AWS account and get information from…
AWS offers many different services, each with different configuration options. With so many options available, there are numerous…
Schrödinger’s Cat and Cybersecurity Alerts
Which vulnerabilities are crucial for your organization, and how do you prioritize them? As we use more technology, finding and fixing…
In many companies, compliance is the main objective of the cybersecurity department. For some, it’s the only reason to invest in…
The recent cyber breach at Microsoft attributed to the China-based threat actor, Storm-0558 is one of the most critical events in the…
One of the challenges in the cybersecurity domain is finding effective, low-cost solutions that are quick to implement and minimize risk…
Cognitive load is one of the biggest challenges of software engineering that affects developers’ productivity and efficiency. Reif (2010)…
The Sysdig Threat Research Team published information about a recently discovered operation called SCARLETEEL. The article explains in…
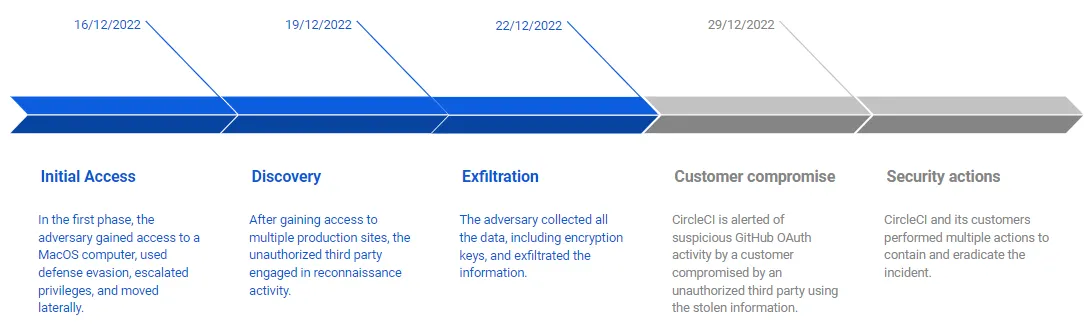
An exercise that helps prioritize security actions based on actual risk and helps us discover weak points is a tabletop exercise (TTX); a…
Cybersecurity is a broad specialization intending to protect computer systems, networks, and sensitive information from digital attacks…
I've also written in Spanish, together with Jose, on donttouchmy.net.
Featured in
22 features across 6 newsletters.
Your weekly roundup of Digital Forensics and Incident Response news
Security engineering newsletter highlighting practical research, tools, and lessons.
All the AWS security news, research, and technical changes in your inbox, every Monday.
The latest news and how-tos in detection engineering.
CloudSecList is the best way to stay on top of the cloud security landscape without being overwhelmed by all the noise.
Increasing efficiency, effectiveness, and OPSEC for security teams worldwide.